Exclusive
Data Centre Infrastructure News & Trends
Data Centre Security: Protecting Infrastructure from Physical and Cyber Threats
Enterprise Network Infrastructure: Design, Performance & Security
Essential Disaster Recovery News for Data Centres
Exclusive
Security Risk Management for Data Centre Infrastructure
Why network resilience now depends on control
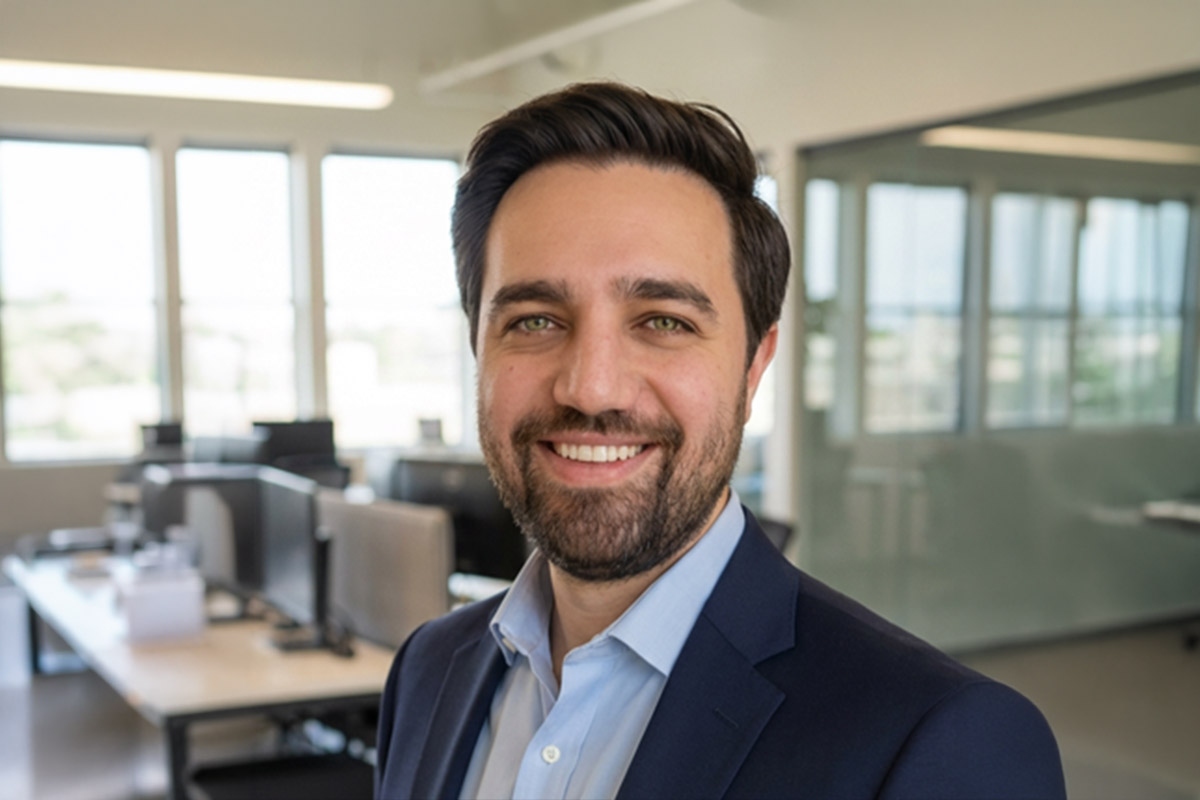
In this exclusive article for DCNN, Ramtin Rampour (pictured above), Principal Solutions Architect at Opengear, explains why independent management access is becoming an essential element of network resilience as data centre environments grow larger, more distributed, and increasingly complex:
Building resilience beyond the production network
With data centres supporting ever higher-density workloads and users increasingly expecting the services they use to be available at all times, network resilience is a fundamental priority for operators responsible for keeping critical infrastructure running.
Resilience is no longer just about whether infrastructure can withstand disruption; it also depends on whether operations teams can retain control when something goes wrong. As data centre environments become more distributed and security-sensitive, the ability to reach critical systems during failure has become central to recovery.
In this context, remote access to networks has become critical. When the network fails, recovery can only begin if teams can still reach the systems they need to fix. A loss of connectivity is no longer only a traffic problem; it can restrict visibility, delay remediation, and leave data centre network teams dependent on the same production environment that is already degraded.
For data centre network teams, resilience now depends not only on network availability, but on maintaining a reliable management path when the production network is degraded or unavailable.
Redundant links and resilient hardware still have a place in delivering this. However, they cannot guarantee recovery on their own. Teams also need a trusted route into critical infrastructure when the production network is misconfigured, compromised, or unavailable. Without it, a familiar fault that should be routine to resolve can become a prolonged recovery exercise.
The control gap
This need for control is becoming more urgent as data centre environments grow increasingly complex. Preventing outages remains a strategic priority for owners and operators, even as infrastructure equipment improves. At the same time, modern architectures and external threats continue to introduce risks that must be actively managed.
For network teams, the takeaway is clear: component reliability alone does not ensure resilience. Effective recovery planning must also address dependency chains, change-related errors, and potential loss of access.
Those dependencies are increasing with AI environments placing heavier demand on traffic inside high-density infrastructure. Edge sites often sit far from specialist engineering teams, whilst hybrid operating models extend the network across owned and hosted environments. Each can lengthen recovery if teams have no independent management path.
During an incident, the gap appears at console level. An engineer may understand which change caused the issue, which device needs attention, or which segment should be isolated, but still have no reliable way to act.
No amount of bandwidth helps if management access depends on the failed route. This gap is exactly what out-of-band management is designed to address. By providing a dedicated, physically separate network path, it gives operators direct console-level and IP access to critical infrastructure, independent of the production network they may need to repair.
Skills, security, and scale
Workforce pressure is another factor widening the control gap. In the 2025 ISC2 Cybersecurity Workforce Study, only 55% of respondents agreed their organisations have the resources needed to address security incidents over the next two to three years.
For data centre operators, that shortage has direct consequences. When incidents occur, recovery often depends on the same network teams that manage access and infrastructure availability. If those teams are stretched, site visits take longer and recovery becomes harder to coordinate.
Stretched data centre network teams need fewer site visits and more repeatable processes. Automation is valuable but it is not a substitute for reachability. A workflow cannot reboot, reconfigure, or isolate a device it cannot access. For large estates, the access model has to be designed before the recovery process can be trusted.
Security adds another constraint. Palo Alto Networks’ 2026 Unit 42 Global Incident Response Report found that identity weaknesses played a material role in almost 90% of investigations, whilst 87% of intrusions involved activity across multiple attack surfaces, including networks.
For data centre operators, this is a network resilience issue as much as a security one. When disruption occurs, teams still need a trusted way to reach routers, switches, firewalls, and other critical devices, but that access cannot rely on the same production network that may be degraded or exposed to attacker movement.
During a cyberattack, management access has to be both available and governed. Speed without strong authentication creates risk. Tight controls with no practical route into the infrastructure slow recovery. Operators need a path that sits outside production traffic, with clear permissions and logs that stand up to audit.
Future-proofing through independent access
Future-proofing data centre networks should start with control under imperfect conditions. An independent management plane separates the route used to control infrastructure from the route carrying production traffic. When the main network is down or untrusted, it allows teams to inspect devices, roll back changes, isolate segments, and verify service health remotely. The aim is not to prevent every failure; it is to prevent failures from removing the operator’s ability to respond.
This capability is valuable from the outset. New infrastructure often needs to be built and secured before normal production connectivity is ready. In edge or remote sites, local intervention can be slow and expensive. In this context, a separate management path allows teams to bring equipment online, test configurations, and reduce dependence on physical access.
Once infrastructure is live, the same path can support daily resilience. Network operations teams can intervene earlier when device health deteriorates and recover services without depending on unstable systems. Against this backdrop, resilience becomes less about emergency improvisation and more about disciplined control built into network operations.
Data centre networks will always face disruption from misconfiguration, cyber threats, equipment faults, and external events. For operators, resilience depends on whether they can retain control when those disruptions occur.
As data centre estates become larger, more distributed, and harder to secure, resilience will depend on a trusted path back into the infrastructure, whether teams are managing a core facility, an edge site, or hosted environments. That control helps teams recover faster and keep critical services always running.
For more from Opengear, click here.

Joe Peck - 8 July 2026
Events
Exclusive
Products
DCNN reports from Johnson Controls' 'Innovation Studio'
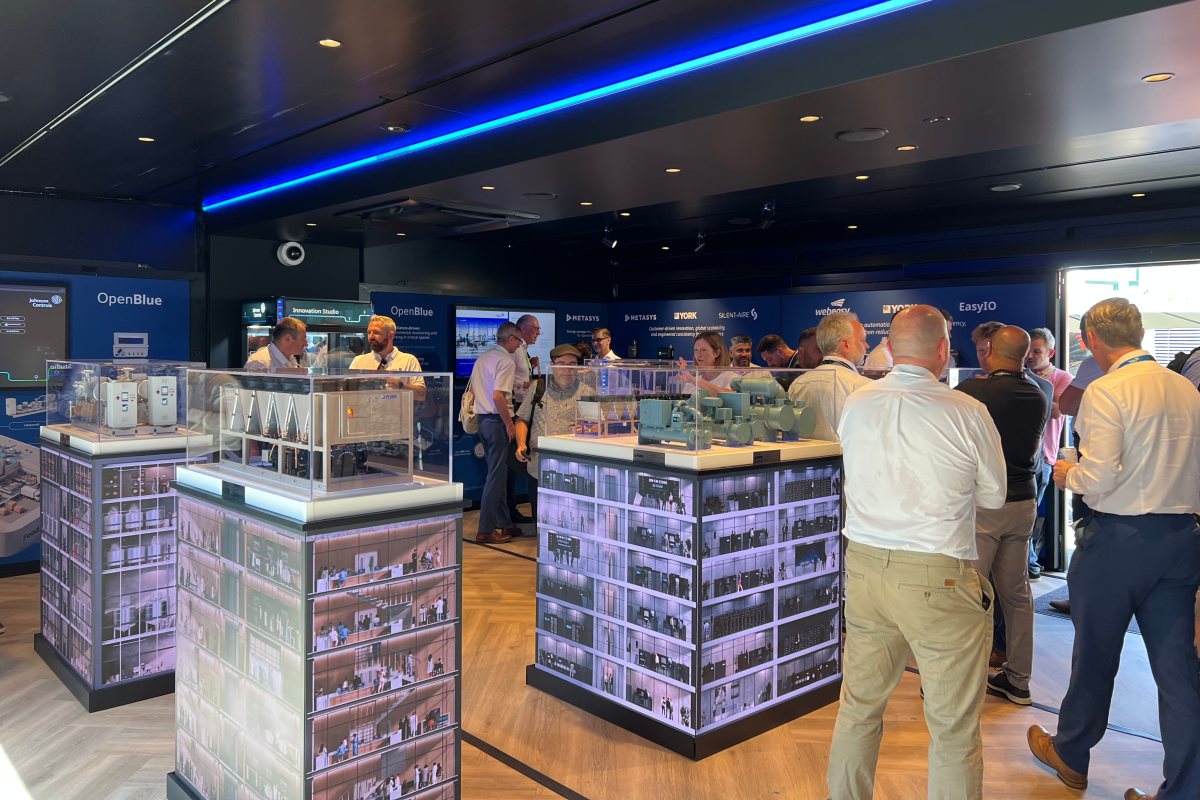
Johnson Controls, a global provider of smart building technologies, brought its travelling Innovation Studio to London between 23 and 26 June, one stop on a 44-city tour taking the company's building technologies portfolio directly to customers, partners, and media across Europe.
DCNN was invited along to step inside the mobile showcase and sit down with John Foley, General Manager, North West Europe at Johnson Controls, whose day job involves leading the company's HVAC team, but whose knowledge stretches across every industry the business serves.
The Innovation Studio itself is the physical expression of an idea Johnson Controls has been mulling for some time: how do you take the collective expertise scattered across the business's European operations and put it in front of every market at once?
John told us, "All of this information, intellectual property, and, more importantly, the experts that come with it are so diffused all around Europe."
The tour, he explains, grew out of conversations between the company's EMEA marketing leadership about how to concentrate that firepower and take it on the road. It is, by his own admission, a fairly bold departure for a company of Johnson Controls' size, but the early results have surprised even the team behind it.
"The engagement with our customers so far has been unbelievable," he continued, adding that appetite has varied (sometimes counterintuitively) from city to city, but has been strong across the board.
Three pillars, one thermal chain
To understand why a HVAC and controls business is investing so heavily in this kind of outreach now, John points to a set of strategic priorities set out by Johnson Controls' chief executive in November 2025: decarbonising the existing built environment, winning in critical environments such as pharmaceutical and biologics production, and enabling what he calls "the future AI economy". It is that third pillar that explains the data centre focus of the London leg.
Johnson Controls has served data centres in one form or another for decades, spanning fire and security, heating and cooling, and building automation. What has changed, John says, is the scale of capital and engineering attention now being directed at the sector as a result of AI-driven growth. The company's pitch to the market has also shifted.
"Our right to win in a data centre, it's not just about cooling; it's actually about our ability to own and also command the entire thermal management chain," he suggested. That means everything from extracting heat at the chip via liquid cooling plates, through rejection and plant-level cooling, all orchestrated through building automation systems.
Heat that does not go to waste
One strand of the conversation that stood out was waste heat reuse, an area in which John argues Johnson Controls' combined HVACR capability (he is careful to stress the "R" for refrigeration) gives it an edge over cooling specialists.
The company's heat pumps, manufactured at its Sabroe facility in Aarhus, Denmark, are already being used across parts of Europe to funnel heat recovered from data centres into district heating networks serving tens of thousands of homes, a practice some Scandinavian countries now effectively mandate for new data centre developments.
John, who lived in Norway for four years, is candid that the UK lags behind on this front. "It's quite frustrating… it's embarrassing," he remarked, though adding that he also sees plenty of opportunity ahead as the conversation matures.
What was on show
That thermal chain philosophy was reflected in the technology on display inside the studio. On the digital side, OpenBlue, Johnson Controls' AI-powered smart building platform, was positioned as the connective layer tying data, insight, and outcomes together across a building's systems, built on the Metasys building automation and controls backbone, alongside the EasyIO Neo controller range and the Webeasy front end.
On the mechanical side, the YORK YVAM air-cooled magnetic bearing chiller was a centrepiece, aimed squarely at hyperscale and colocation cooling loads and built to run efficiently across a wide ambient range without relying on free-cooling coils, alongside the YCPB heat pump range for lower-carbon heating and cooling.
Representing the industrial refrigeration side of the business, the Sabroe DualPAC combines the company's ChillPAC and HeatPAC units into a single modular heat pump, aimed at applications needing both cooling and high-temperature heat output efficiently.
Bringing it to the UK
Wrapping up, John returned to the purpose of the tour itself: getting Johnson Controls' engineers and technology in front of customers who might otherwise only encounter the brand through a single product line.
Given the scale of change facing UK data centre operators, from AI-driven density increases to mounting pressure on energy and water use, it is a conversation that feels timely, and one that DCNN expects to keep returning to as the Innovation Studio continues its European run.
For more from Johnson Controls, click here.
Joe Peck - 2 July 2026
Data Centre Operations: Optimising Infrastructure for Performance and Reliability
Data Centre Software for Smarter Operations
Exclusive
Features
News in Cloud Computing & Data Storage
What European data sovereignty means for data centre tools
In this exclusive article for DCNN, Swiss privacy technology company Proton Mail examines why evolving European data sovereignty requirements are forcing data centre operators to reassess the tools they use to manage infrastructure, store operational data, and demonstrate regulatory compliance:
Data sovereignty moves into the data centre
For most data centre teams, the concept of data sovereignty has lived at a comfortable arm's length. It was something legal worried about, something the sales team put in proposals, something that got mentioned at vendor briefings before the coffee break. But that distance is collapsing, and fast.
The European Union's regulatory architecture around data has shifted from a set of compliance checkboxes into something far more structural. GDPR established the foundations; the EU Data Act, the Data Governance Act, and the ongoing ripple effects of transatlantic legal friction (particularly the tensions created by the US CLOUD Act) have built several more floors on top of it. The result is a framework that increasingly determines not just what data your organisation holds, but which tools you are permitted to use to manage, transfer, share, and store it.
This has direct, practical consequences for data centre operations teams. The monitoring platform you log into each morning, the cloud storage your engineers use to share runbooks, the ticketing system where incidents are logged, the collaboration suite where shift handovers happen: if any of these tools are operated by a company headquartered outside the EU, they may now carry a compliance risk that regulators are no longer prepared to overlook. As explored in a broader look at why data security is no longer optional, the costs of underestimating this shift go well beyond fines.
The sovereignty problem in plain terms
Data sovereignty, at its core, is the principle that data generated within a jurisdiction should remain subject to that jurisdiction's laws, regardless of where it is physically stored or which company's servers it sits on. In the EU context, this means that personal data relating to European citizens and businesses should not be accessible to foreign governments or legal systems without going through EU legal channels and oversight.
The complication arises from the US CLOUD Act, signed into law in 2018. This legislation grants US authorities the power to compel American technology companies to hand over data, even data stored on servers in Europe, without necessarily requiring a formal mutual legal assistance treaty process. For a European organisation using a US-headquartered SaaS provider, this creates what regulators have called an active legal paradox: data that appears to be stored safely in an EU data centre may still be legally accessible to a non-EU government.
It is a risk that regulators across France, Germany, the Netherlands, and beyond are treating with increasing seriousness. Enforcement actions against US cloud providers by national data protection authorities have grown steadily, and the appetite for leniency is diminishing.
Where operations teams feel it
The challenge for data centre teams is that the operational tooling that makes modern facilities function efficiently has, over the past decade, migrated almost entirely into the cloud - and largely into platforms operated by American technology companies. This was a rational progression: the tools were excellent, the pricing was competitive, and the compliance requirements, while present, were manageable.
That calculus is changing. The categories of software that carry the most exposure include:
• DCIM platforms — If telemetry, asset data, or incident records are routed through non-EU cloud infrastructure, they may be subject to foreign access requests.
• Ticketing and ITSM systems — Incident logs can contain sensitive operational and customer data, and where these records are stored and processed matters legally.
• Collaboration and file-sharing tools — Runbooks, change documentation, and engineering notes shared via US-headquartered platforms may not satisfy GDPR data processing requirements.
• Monitoring and observability platforms — Network performance data, access logs, and infrastructure health metrics can constitute sensitive data under certain regulatory interpretations.
• Email and calendar services — Operational communications may be covered by data residency requirements, particularly in regulated sectors such as finance or healthcare.
The question teams are increasingly being asked by compliance officers, enterprise customers during audits, and regulators during inspections is not simply "is this data encrypted?" but "under whose legal jurisdiction does this data sit, and who could compel access to it?" Industry voices have been making this point for some time, as reflected in commentary gathered on Data Privacy Day, where the emphasis fell squarely on building repeatable operational controls rather than chasing individual compliance milestones.
The sovereign cloud push
The response from the market has been a wave of "sovereign cloud" offerings: architecture models where infrastructure, operational staff, and legal entities are all resident within the EU, and where data is contractually and technically ringfenced from parent-company access in non-EU jurisdictions.
Several major hyperscalers have invested heavily in these products. Microsoft's EU Data Boundary, Google's Sovereign Controls, and AWS's EU Sovereign Cloud are all attempts to provide assurances that European data will not traverse US legal jurisdiction. Whether these assurances are sufficient, given that the parent companies remain subject to US law, remains contested amongst legal scholars and regulators. Germany and France, in particular, have pushed back on the idea that a US company's technical commitments can fully override a foreign court order.
The EU's Gaia-X initiative represents the most ambitious attempt to build a native alternative: a federated, interoperable digital infrastructure that reduces dependency on non-European hyperscalers entirely. Progress has been slower than its architects hoped, but the framework it has established around transparency, portability, and provenance of data is increasingly influencing procurement decisions at large European enterprises and public sector bodies. The physical reality of where infrastructure actually sits remains critical to all of this, a point underlined by the lessons drawn from the OVHCloud fire, which demonstrated how quickly assumed protections can evaporate when something goes wrong at the hardware level.
Rethinking the toolchain
For data centre teams, the practical consequence is a growing need to audit the toolchain - not just the infrastructure they manage for customers, but the tools they use internally to manage that infrastructure.
This is a non-trivial task. Many of the most capable platforms in categories like monitoring, ITSM, and collaboration are US-headquartered. Replacing them wholesale is expensive, disruptive, and technically risky. The more pragmatic approach being adopted by many European operators is a tiered assessment: identifying which tools handle which categories of data, and which of those data categories carry the highest regulatory exposure.
Operational telemetry that contains no personal data may carry a different risk profile than a shared drive full of customer documentation, change records, and contractual files. The latter category (documents and files shared amongst engineering and operations teams) is one where the market for European-origin alternatives has matured considerably.
For file storage and document sharing specifically, a number of privacy-focused alternatives have emerged that offer end-to-end encryption, EU-based infrastructure, and no exposure to US jurisdiction. Proton Drive is one example; being built on zero-access encryption and hosted under Swiss and EU law, it is designed so that even the service provider cannot access the contents of stored files. For operations teams handling sensitive engineering documentation or customer-related records, this kind of architecture addresses the sovereignty question at a technical rather than contractual level.
The distinction between technical and contractual sovereignty protections is one that regulators are increasingly paying attention to. A Data Processing Agreement with a US cloud provider commits that provider contractually to certain behaviours; zero-access encryption means that no behaviour, however compelled, can result in plaintext data being handed over, because the keys never leave the customer's control.
The compliance burden on operations
What makes this period particularly challenging for data centre teams is that sovereignty compliance is not a one-time project; it is a continuous risk assessment process, one that requires keeping pace with an evolving regulatory landscape across multiple EU member states.
Germany alone layers 17 state-level data laws on top of national and EU requirements. The practical implication is that an operations team running a facility serving customers across multiple European jurisdictions may need to maintain a sophisticated, jurisdiction-aware view of where data flows, which tools touch it, and which legal regimes apply. The full scope of what that means for day-to-day operations is covered across DCNN's compliance coverage.
This is driving demand for a new kind of capability within operations teams: compliance literacy, meaning engineers who understand not just how to configure a monitoring platform, but what data that platform collects, where it sends it, and whether that is consistent with the data processing agreements their organisation holds with its customers.
The audit pressure is already here
Customer-driven audit pressure is one of the most immediate ways data centre teams are encountering sovereignty requirements in practice. Enterprise customers, particularly those in regulated sectors like finance, healthcare, and government, are increasingly including detailed data residency and toolchain questions in their due diligence processes before signing colocation or managed service contracts.
They want to know not just where their data sits, but which third-party tools the data centre operator uses to manage access, monitor systems, and handle incidents, because those tools are part of the data processing chain. A data centre that stores customer data on EU infrastructure but logs all incident management activity through a US-based ITSM platform may have a harder time satisfying those audits than one that has thought carefully about the full operational stack. This connects directly to the broader operational challenges outlined in an earlier look at the key pressures facing data centre operations teams, where compliance and ESG demands were already competing for finite team bandwidth.
Looking ahead
European data sovereignty is not a temporary regulatory moment; it reflects a deep structural shift in how European governments, regulators, and enterprise customers think about digital infrastructure, one in which the origin and legal jurisdiction of technology matters as much as its performance or price.
For data centre teams, this means the toolchain review is not optional. The platforms that operations, engineering, and management teams use every day are now part of the compliance picture. The good news is that the market for sovereign-by-design tooling is expanding, covering everything from monitoring and observability to file storage and secure communications.
The teams that will navigate this most successfully are those that start the audit now, before a customer inquiry, a regulatory inspection, or an incident forces the issue. Understanding which tools handle which data, under whose jurisdiction, and with what level of technical protection is not just a compliance exercise; it is increasingly a competitive differentiator.
Joe Peck - 1 July 2026
Data Centre Business News and Industry Trends
Exclusive
Insights into Data Centre Investment & Market Growth
AI infrastructure is booming beyond the bubble
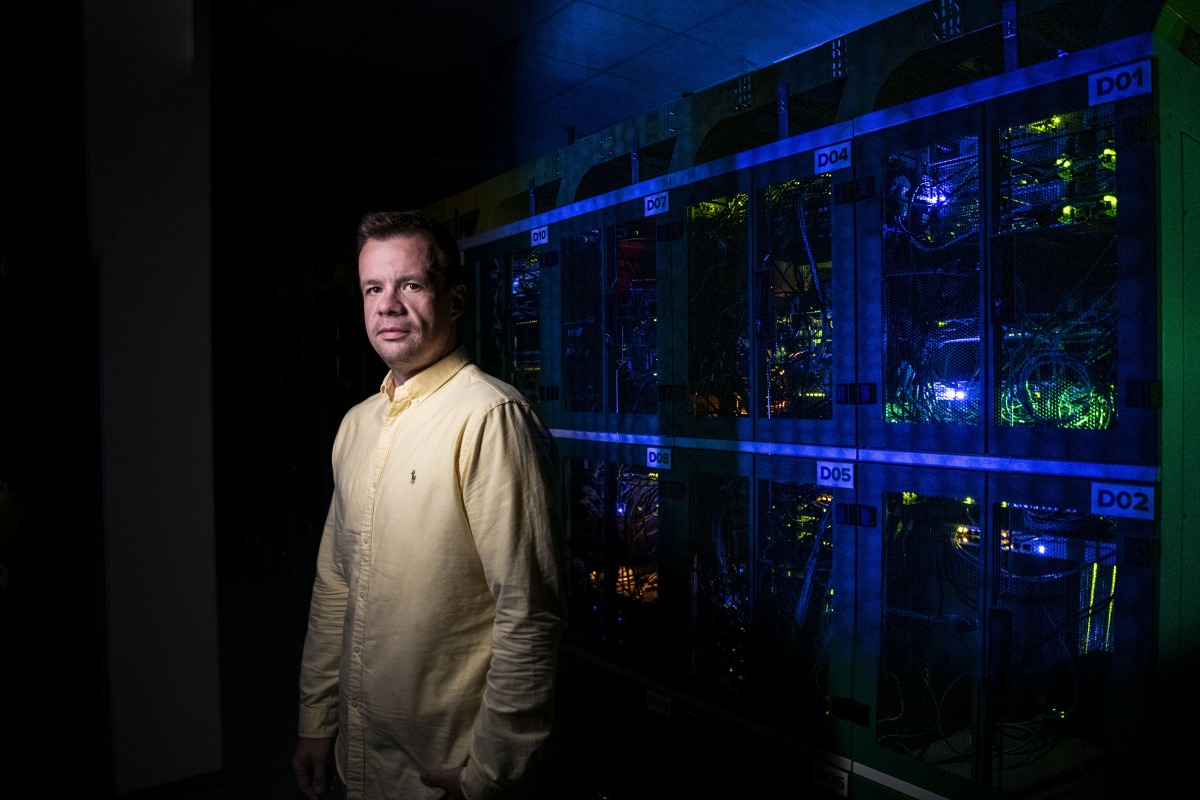
In this exclusive article for DCNN, Damir Špoljarič (pictured above), founder of Gi21 Capital, challenges the idea of an AI bubble, suggesting that long-term investment in data centre infrastructure reflects enduring demand rather than short-term market speculation:
The distinction between applications and infrastructure
Every conversation about the economics of AI inevitably arrives at the subject of the dreaded AI bubble. Artificial intelligence, we’re told, is a bubble that is just moments from bursting. When the MIT Sloan Management Review compiled its list of the biggest trends in AI and data science for 2026, the deflation of said bubble topped the list. With the IPO race between OpenAI and Anthropic heating up, The Telegraph worried aloud about “history repeating itself” with the “dotcom bubble 2.0”.
But these conversations are conflating two distinct categories: AI infrastructure and AI applications. The bubble-indicating hype exists predominantly at the application layer, consisting of AI startups, software platforms, and emerging business models. Infrastructure, by contrast, is driven by non-cyclical demand and is still in the early stages, so it’s more stable than the application layer. The entire AI ecosystem isn’t a single market; therefore, there is no single bubble that can burst.
The physical foundation that makes AI possible (data centres, power systems, networking equipment, cooling technologies, and compute capacity) and the investment appear increasingly structural and long-term.
Valuation vs demand vs implementation
Many AI companies are without a doubt overvalued, lacking strong fundamentals for such valuation, and those company-sized bubbles may indeed burst. However, there is no industry-sized bubble, and it’s a mistake to conflate the failure of individual companies with the long-term trajectory of AI adoption itself.
No bubble changes the reality that AI is still in the early stages of implementation across all industries globally, and that it will have a profound effect on the social contract in the coming years. This is real, transformative technology that will create far more winners than failed companies.
The models are getting more efficient by the day, but this does not mean that it will soon outpace demand. The world is likely using only a minuscule fraction of the AI that will eventually be deployed. A McKinsey report released last November found that nearly two thirds of organisations are still in their AI pilot and experimentation stages, and have not yet begun proper scaling across their enterprises.
As AI progressively penetrates every industry, the need for infrastructure will appear increasingly sensible and structural as opposed to speculative. Efficiency gains don’t change the fact that AI adoption remains at a very early stage, with untold demand yet to be realised.
Not-so-peak investment
The validity of any argument about an AI bubble rests on the idea that the industry is at, or near, peak investment. At best, we’ve only just finished the warm-up. There are indeed exorbitant amounts of capital flowing into foundation models, but that’s to be expected when building the base infrastructure layer of a technology as transformative as this.
It’s also necessary. We’re building the infrastructure required for future growth, not responding to already realised demand. Data centres, power grids, transmission networks, and compute clusters are years-long projects from planning to construction. Entire economies would struggle with capacity shortages if we waited until demand fully materialised. Consider it the opening phase of a much longer infrastructure buildout.
The cash flow is justified when viewed as front-loading the infrastructure of the biggest industrial shift of the century. Although AI is mostly limited to software, its next phase will be real-world, physical integration, particularly through robotics. Once that occurs, an even bigger (and more obviously justified) explosion in capital volume is likely to occur. Autonomous, AI-driven robotics will become central to manufacturing, logistics, and daily life, and require a capital expenditure that makes today’s spending look tiny.
Real demand and imagined bubbles
Supply constraints are good evidence that infrastructure demand remains strong, but it’s also more complex than that. Global project delays often come down to the limited availability of critical data centre infrastructure components such as transformers and UPS batteries. Lead times for both typically exceed a year. GPU supply is under hard pricing pressure due to high demand. Such realities are wholly inconsistent with the concept of a market suffering from excess capacity.
The likelihood of overbuilding is low. Genuine long-term demand exists behind current infrastructure development. Decade-long contracts are now commonplace in this market. Speculative projects haven’t disappeared, but overall financing conditions remain relatively disciplined. To that end, banks and infrastructure investors remain relatively conservative when it comes to financing, insofar as they still want to see meaningful long-term customer commitments before backing new AI data centre developments.
Infrastructure is always built ahead of demand - only with AI has this fact inspired such panic. The gap between current end-user consumption and projected future demand is fairly standard in the tech world.
Less bubble, more well-laid plans
Rather than view AI infrastructure as a bubble, we should view it as akin to city planning. Roads and water pipelines are built before they’re demanded en masse, and demand follows their construction. Construction and deployment take time. AI infrastructure, like any other kind of infrastructure, must be planned years in advance.
The bubble is not about to burst, because the bubble doesn’t exist. This is only the beginning of development, implementation, and investment. However it looks in a decade, it is not cause for frantic concern today.
Joe Peck - 29 June 2026
Data Centre Infrastructure News & Trends
Exclusive
Innovations in Data Center Power and Cooling Solutions
Why the UK’s AI ambitions demand a new power paradigm
In this exclusive article for DCNN, Javier Cavada (pictured above), President & CEO EMEA at Mitsubishi Power, considers how private power networks and on-site generation could help data centre operators overcome grid constraints while supporting the UK's AI ambitions:
Decoupling digital growth
In the UK, expanding digital and AI infrastructure is a strategic priority. The Government has indicated that the country will need at least 6GW of AI-capable data centre capacity by 2030 to support this ambition.
However, this digital growth is outpacing the capacity of the UK’s physical energy infrastructure, resulting in a growing mismatch between the country’s AI ambitions and the systems needed to support AI-powered data centres.
Electricity demand from data centres is already significant, at a time when the wider economy - indeed, society as a whole - is rapidly electrifying. Currently, data centres account for around 6% of UK electricity consumption, and the National Energy System Operator (NESO) projects that this could increase to 8.8% by 2030 as AI adoption accelerates.
At the same time, grid connection requests for demand-side projects have surged from around 41GW in late 2024 to 125GW by mid-2025, with approximately 50GW linked to data centre developments. This rapid build-up in the connection queue is creating significant congestion, with some large, high-capacity projects now facing delays of up to a decade.
All of this has prompted regulatory intervention, with NESO moving away from the previous “first come, first served” approach towards a more selective “first ready, first served” model for prioritising connection requests.
While this shift is welcome, it will take time to translate into tangible improvements on the ground. In the meantime, the key takeaway for developers is clear: securing a guaranteed power connection has become a far more significant constraint on new data centre development than access to land.
More broadly, the structural limitations of the UK’s centralised and ageing grid are emerging as a major barrier to delivering on the country’s AI and digital infrastructure ambitions.
The grid bottleneck and the competitiveness risk
The reality is that to ensure operational uptime from day one, operators can no longer rely solely on the UK’s national grid. Instead, delivering the power required to build and operate this critical infrastructure will increasingly depend on on-site energy parks and dedicated private-wire networks.
This challenge extends well beyond a single industry; it is fundamental to the UK’s ability to sustain a dynamic, modern economy. AI, cloud computing, and high-performance computing (HPC) have become core drivers of global competitiveness, and, in turn, access to reliable power is a decisive factor in where hyperscalers and technology firms choose to deploy capital.
These decisions shape long-term job creation and regional economic growth. Without sufficient power availability, the UK risks losing major digital investments - as well as the high-skilled employment they bring - to leading European markets.
Competitors in the Netherlands, Ireland, and the Nordics are gaining ground by offering faster access to power - a trend already evident in the Slough/M4 corridor, where connection moratoriums have pushed operators to look beyond traditional hubs simply to keep pace with demand.
One response is the deployment of high-efficiency gas turbine systems to help bridge this capacity and infrastructure gap. Gas turbines provide a practical interim solution, delivering reliable, dispatchable power at scale today while offering a pathway to lower-carbon operation as hydrogen and other low-carbon fuels mature.
Why private power models are becoming essential
By connecting dedicated power assets directly to the data campus via private-wire networks, operators can bypass multi-year utility queues, significantly compress construction timelines, and secure a predictable envelope of capacity. Operating behind the meter also provides a critical commercial advantage, shielding multi-million-pound infrastructure investments from volatile wholesale market prices and localised grid congestion, as well as enabling greater long-term cost certainty.
However, access to power alone does not fully resolve the challenge. AI workloads require continuous, 24/7 baseload stability - something intermittent renewables cannot deliver in isolation.
As the UK continues to scale wind and solar generation, managing intermittency becomes an increasing constraint, reinforcing the role of on-site gas turbines in providing immediate, dispatchable power to stabilise private networks.
Crucially, deploying on-site gas generation does not mean abandoning sustainability goals. Instead, it offers a pragmatic bridge to net zero. The industry is already shifting towards flexible thermal infrastructure that can meet current demand using natural gas, while remaining compatible with lower-carbon fuels.
Modern high-efficiency gas turbines, for example, can already operate on a 30% hydrogen blend, with engineered pathways to 50% and ultimately 100% hydrogen capability from around 2030 onwards, as technology and fuel supplies mature. This ensures that assets deployed today remain viable in a decarbonised future.
Embracing a new model of infrastructure self reliance
The UK cannot become a global AI leader if its data centres remain dependent on an increasingly constrained public grid. Colocated energy parks represent a shift from grid dependency to infrastructure self-reliance. By deploying on-site generation, operators can decouple build timelines from grid constraints while laying the foundations for a more resilient, future-ready, low-carbon digital economy.
In this context, digital sovereignty cannot wait for grid reinforcement. The sector is moving towards a model in which operators take greater control of their energy supply, ensuring both immediate resilience and long-term strategic flexibility.
For more from Mitsubishi, click here.
Joe Peck - 25 June 2026
Cyber Security Insights for Resilient Digital Defence
Data Centre Security: Protecting Infrastructure from Physical and Cyber Threats
Exclusive
Why the inbox is becoming the weakest link in DC security
As AI accelerates demand for digital infrastructure, data centre operators are investing heavily in power, cooling, and resilience. Yet, while the industry focuses on physical infrastructure challenges, one of the most common and effective cyberattack methods remains far more familiar: email.
In this exclusive article for DCNN, Billy McDiarmid, VP Customer Engineering at Red Sift, argues that phishing, impersonation, and supply-chain email attacks are becoming an increasingly serious risk for operators managing high-value AI workloads and complex partner ecosystems:
Email security
The data centre industry is in the middle of an unprecedented expansion that is unleashing economic growth across the United Kingdom, creating more than 43,000 jobs, according to Datum.
Still, with AI workloads driving historic demand for power, cooling, and high-density computing, operators are racing to accommodate new capacity. As a result, the UK Government is fast tracking planning approvals, with entire regions repositioning themselves as AI infrastructure hubs through the UK’s AI Growth Zones. Yet, amid this rapid growth, the industry is overlooking a threat that is far more mundane than liquid cooling, grid constraints, or even expansion protests.
For all the advancements of modern data centre design, the most common entry point for attackers going after network security is still the inbox. Today, email remains the primary vector for things like phishing, impersonation, and invoice fraud. As AI accelerates both the value of data centre workloads and the sophistication of cyberattacks, the gap between physical resilience and basic things like email security is becoming a critical vulnerability.
Modern data centres are complex ecosystems of operators, contractors, equipment vendors, and service partners. Every one of these relationships is mediated through email, and when attackers impersonate a supplier, mimic an executive, or compromise a contractor’s mailbox, they gain a direct path into the operational heart of a facility. A single fraudulent email can trigger misconfigurations, grant unauthorised access, or divert critical payments. These are not hypothetical scenarios; they are the most common form of cyberattack across infrastructure-reliant industries, according to the NCSC. And the threat now extends beyond the inbox. Just last year, attackers created a domain impersonating a logistics platform used by UK freight brokers, causing significant operational disruption and financial losses, with estimates ranging from £40,000 to £160,000 per incident.
AI is increasing the sophistication of attacks
Now, with the cost of entry for bad actors at near zero, AI is only exacerbating the problem. Attackers can now generate highly convincing phishing messages tailored to specific individuals, roles, or organisations. They can scrape public data to mimic writing styles, automate reconnaissance, and craft messages that bypass traditional filters. Deepfake audio and video add another layer of credibility to fraudulent requests. The result is an environment where even experienced professionals struggle to distinguish legitimate communication from malicious intent.
At the same time, the value of what sits inside data centres has never been higher. AI models, training datasets, and proprietary algorithms represent some of the most valuable intellectual property in the world. A breach that once disrupted a handful of virtual machines can now compromise entire AI pipelines. This makes data centre operators and their supply chains irresistible targets. And because email is the easiest and cheapest attack vector to exploit, it is where attackers focus their efforts.
Email security must become baseline infrastructure protection
The industry has invested heavily in physical security, redundancy, and environmental resilience. Ironically, email security has not kept pace.
For the UK, this is not just a corporate hygiene issue; it is about network security and ensuring trust behind the country’s most iconic industries. Enforcing modern email authentication standards, such as email security across data centre operators and their supply chains, must be treated as a baseline security requirement, not an optional control left to individual organisations. Unfortunately, according to a recent analysis at Red Sift, over 39% of the top organisations in the UK are not enforcing DMARC.
With foreign threats on the rise, the status quo that viewed email security as 'nice to have' is no longer tenable. It is a real world infrastructure risk, just like locking the front door to the building. If an attacker can impersonate a trusted partner, they can influence operational decisions. If they can compromise a contractor’s account, they can gain access to sensitive systems.
And because data centre operations depend on a vast network of suppliers, these standards must extend across the entire ecosystem, not just within the operator’s perimeter.
Regulation is pushing security higher up the agenda
Recent regulations are starting to move in this direction. The UK Government, as well as those around Europe, are tightening requirements around identity verification, communication security, and supply-chain resilience. It is also pushing forward on the Cyber Security and Resilience bill, an important step in this direction. As AI becomes more central to national infrastructure, these expectations will only grow. Operators who invest early in robust email security will be better positioned to meet emerging compliance demands and to reassure customers that their most sensitive workloads are protected.
Enterprises choosing where to host their AI workloads want to know that partners are resilient not only in physical infrastructure but in digital channels as well. The future of data centre resilience depends on recognising that the inbox is not a theoretical risk; it is the front line, just as the security guard out front is.
As the AI era accelerates, the industry must build not only bigger and more efficient facilities, but safer and more trustworthy communication systems. Email may be one of the oldest technologies in the digital world, but securing it is one of the most urgent challenges facing the data centre sector today.
Joe Peck - 22 May 2026
Data Centre Architecture Insights & Best Practices
Data Centre Build News & Insights
Data Centre Projects: Infrastructure Builds, Innovations & Updates
Exclusive
'DC construction enters a new era of delivery pressure'
In this exclusive article for DCNN, Dave Wagner, VP of Product Marketing at Newforma, examines how AI-driven demand, compressed timelines, and constantly evolving designs are forcing construction teams to rethink how data centre projects are coordinated and delivered:
Why construction teams are rewriting the playbook
The data centre boom has pushed construction into unfamiliar territory. Demand keeps climbing, driven by cloud computing, AI workloads, and real-time digital services. Analysts expect the global data centre market to pass $500 billion (£369 billion) within the decade. That growth sounds like opportunity; on the ground, it feels like pressure.
Project teams face a new reality: Designs shift mid-build, stakeholders span continents, precision requirements leave no room for error, timelines shrink, and the old workflows do not hold up under these conditions. The solution isn’t just to work harder; it’s to work differently.
The golden thread is under strain
The “golden thread” promises a clear, traceable record of decisions from design through to delivery. In data centre projects, that thread gets pulled in every direction.
Designs evolve while construction is already underway and a change in server density drives new cooling requirements. That then triggers updates across mechanical and electrical systems, while documentation must reflect those changes in real time or the thread breaks.
Carl Veillette, Chief Product Officer at Newforma, sees this first hand, stating, “On data centre projects, the golden thread is not a static record; it is a live system. If it falls out of sync with reality, the risk compounds fast.”
When information lags, teams build off outdated assumptions. That leads to rework, delays, and finger-pointing. Maintaining continuity of information is no longer a compliance exercise, but a delivery requirement.
Design does not sit still
Traditional construction relies on a stable design phase. Data centres ignore that sequence as technology advances too quickly. A facility planned around one generation of hardware often needs to support the next before completion. GPU-heavy AI workloads increase power density while liquid cooling replaces air in certain zones and redundancy strategies evolve.
Each shift forces coordination across disciplines:• Electrical systems must handle higher loads.• Cooling infrastructure must adapt to new methods.• Structural layouts must support revised equipment footprints.
These are not minor tweaks; they affect core systems.
Carl puts it plainly, “You are designing for a future state that keeps changing. The teams that succeed are the ones that accept that volatility and build processes around it.”
That means parallel workflows. Design, coordination, and construction happen at the same time, whilst decisions move faster, often with incomplete data. Teams need immediate visibility into the latest information to stay aligned.
Precision, security, and uptime raise the stakes
Data centres operate under strict conditions. Downtime is not tolerated and systems must perform on day one. This drives extreme precision:
• Redundant power systems must function without failure.• Cooling must maintain exact environmental conditions.• Security measures must meet strict standards.• System integration must be flawless.
At the same time, security concerns limit information access. Teams must share data widely enough to stay aligned while also restricting sensitive details. The margin for error disappears.
According to Uptime Institute, over 60% of data centre outages cost more than $100,000 (£74,000), with a growing share exceeding $1 million (£739,000). That risk shapes every decision. Teams cannot afford mistakes caused by poor coordination or outdated information.
Speed to market is the new benchmark
The race to bring capacity online has compressed schedules across the industry. Hyperscale operators push for faster delivery to meet demand, and delays translate into lost revenue and competitive disadvantage. This pressure reshapes project timelines:
• Design cycles shorten.• Construction phases overlap.• Procurement accelerates.• Commissioning windows tighten.
There is no buffer for inefficiency. Rework becomes expensive and miscommunication becomes costly.
Carl highlights the impact, noting, “Speed to market is not a goal anymore; it is the baseline. The only way to hit it is to remove friction from how teams share and act on information.”
A shift towards structured collaboration
The common thread across these challenges is information flow. Projects succeed when the right data reaches the right people at the right time. That requires a shift in how teams manage project information:
• Centralised access to current documents and models• Clear tracking of RFIs, submittals, and decisions• Real-time updates across all stakeholders• A complete audit trail for accountability and risk management
This is where platforms like Newforma play a role. They support the golden thread by keeping project information connected, traceable, and accessible.
The impact shows up in reduced risk and faster delivery. Teams spend less time searching for information and more time acting on it. Coordination improves and errors drop, whilst projects move forward with fewer disruptions.
The new standard
Data centre construction has set a new standard for the industry. It demands speed without sacrificing precision. It requires flexibility without losing control. It depends on collaboration at a scale most projects never reach.
These conditions will not ease, as demand will keep rising and technology will keep evolving.
The teams that adapt their workflows to this reality will keep pace. Those that do not will fall behind. The playbook has already changed. The only question is who is still using the old one.
Joe Peck - 14 May 2026
Data Centre Business News and Industry Trends
Data Centre Infrastructure News & Trends
Exclusive
Infrastructure Management for Modern Data Centres
Insights into Data Centre Investment & Market Growth
Navigating AI’s infrastructure surge
In this exclusive interview, DCNN speaks with Lottie Westerling (pictured above), Head of Product at techoraco, about the structural pressures emerging across digital infrastructure, the industry’s shifting priorities, and the debates set to define the next phase of AI-driven growth:
Power, talent, and the road ahead
DCNN: AI is accelerating demand for digital infrastructure at an unprecedented rate. From your perspective, is the industry genuinely keeping pace, or are we starting to see structural gaps emerge?
Lottie: The pace of growth across digital infrastructure is unlike anything the industry has experienced before. AI has accelerated demand dramatically, and we’re seeing a surge of activity from both established players and new entrants looking to capitalise on the opportunity.
However, this rapid expansion is also exposing clear structural gaps - most notably around access to power. The challenge is no longer just about building capacity, but about how quickly that capacity can be energised. From the resurgence of gas and the resulting pressure on turbine supply to increasingly long grid interconnection queues, the strain on energy infrastructure is becoming more visible.
In many ways, demand is now outpacing the systems that support it - permitting, power delivery, and supply chains alike. Addressing these constraints will be critical for organisations that want to remain competitive in an AI-driven landscape.
DCNN: Events like Datacloud Global Congress Cannes bring together a wide cross-section of the ecosystem. What recurring themes are you hearing most often from industry leaders today?
Lottie: Several themes are consistently coming to the fore in conversations with industry leaders. As already mentioned, speed to power remains a dominant concern, but it’s closely followed by a broader shift in how data centres are being designed.
As density requirements increase, we’re seeing a growing focus on new architectures, with liquid cooling becoming central to future-ready design strategies. At the same time, financing continues to be a key topic - not due to a lack of capital, but because of questions around risk allocation and the long-term bankability of large-scale projects.
Talent continues to dominate as another major area of concern. The rise of AI-driven “gigafactories” is intensifying demand for skilled workers, and the shortage of talent is becoming just as critical as constraints in equipment or infrastructure.
Finally, community engagement is rising on the agenda. Public perception and planning friction are increasingly influencing project timelines, making it essential for the industry to communicate its value more clearly and responsibly.
DCNN: The industry is often described as highly collaborative, yet also competitive. How important is collaboration in addressing some of the sector’s biggest challenges, such as energy access or skills shortages?
Lottie: Collaboration is fundamental to solving the industry’s most pressing challenges. Issues such as energy access extend far beyond the data centre sector; they sit at the intersection of grid planning, regulation, power generation, and infrastructure design. As a result, meaningful progress depends on close coordination between the energy ecosystem and digital infrastructure stakeholders.
The same principle applies to talent. Addressing the skills gap will require a collective approach, from developing shared training pathways to increasing visibility into career opportunities across the sector. By working together, the industry can make these pathways more accessible and attractive to a broader, more diverse workforce.
DCNN: Talent continues to be a critical issue across digital infrastructure. What changes are needed to attract and retain the next generation of talent into the sector?
Lottie: One of the biggest challenges is awareness. The value proposition of a career in digital infrastructure is not always well understood, particularly among younger audiences. There is a clear need to better communicate the scale, impact, and long-term opportunity that the sector offers.
This means investing in more structured entry points such as graduate programmes, apprenticeships, and industry-led initiatives that make it easier for people to find and pursue careers in the space. It also involves creating clearer career pathways and showcasing the diversity of roles available, from engineering and operations through to sustainability and innovation.
Ultimately, attracting the next generation will depend on making the industry more visible, more accessible, and more aligned with the priorities of emerging talent.
DCNN: From the conversations you’re helping to shape across the Global Congress community, are you seeing a shift in priorities?
Lottie: There is a growing sense of cautious optimism across the industry. While demand remains strong, there is an increasing focus on ensuring that growth is both resilient and sustainable over the long term.
Leaders are placing greater emphasis on the fundamentals: reliability of power supply, sustainability of water usage, and alignment with evolving regulatory frameworks. There is also a stronger focus on future-proofing assets, ensuring that infrastructure built today will remain relevant as technologies continue to evolve.
This suggests a shift from purely rapid expansion towards a more balanced approach that prioritises durability, efficiency, and long-term viability.
DCNN: Looking ahead, what topics or debates do you think will define the next 12–24 months in the data centre and digital infrastructure space?
Lottie: Over the next 12 to 24 months, several key debates are likely to shape the direction of the industry. At the forefront is how to meet the enormous power requirements of AI at scale. This includes discussions around alternative energy pathways, the role of nuclear, and the viability of behind-the-meter solutions.
Risk allocation will also be a central issue, particularly in how responsibility is distributed between investors, operators, and tenants in increasingly complex projects.
At the same time, more forward-looking topics are beginning to gain traction. The potential for data centres in space, while still nascent, is generating discussion, as is the longer-term impact of quantum computing on infrastructure requirements.
Together, these conversations reflect an industry that is not only responding to immediate pressures, but also actively shaping its future trajectory.
Joe Peck - 11 May 2026
Data Centre Business News and Industry Trends
Data Centre Compliance: Standards, Risk & Governance
Data Centre Infrastructure News & Trends
Data Centre Regulations & UK Compliance Updates
Enterprise Network Infrastructure: Design, Performance & Security
Exclusive
How to ensure your infrastructure complies with DORA
In this exclusive article for DCNN, Chris Noon, Director of Solution Engineering, International at Alkira, outlines how financial institutions must embed security, resilience, and transparency into their network infrastructure to meet the demands of DORA:
Rethinking network infrastructure
The Digital Operational Resilience Act (DORA) marks a major change in how the European financial sector manages technology risk. Instead of focusing only on solvency, DORA emphasises keeping digital services running smoothly. For enterprise organisations, this means every part of the technology stack, especially the network infrastructure connecting cloud environments and data centres, must be reviewed with operational resilience and security in mind.
With this new framework, financial institutions are ultimately responsible for their digital resilience, even as they rely more on a complex network of ICT third-party service providers. To manage this, IT and compliance teams need to shift from reactive security to building systems where resilience is built in from the start.
The core pillars of DORA compliance
DORA requires financial organisations to have a complete strategy for managing ICT risks. This strategy should address five main areas: ICT risk management, incident reporting, operational resilience testing, third-party risk management, and information sharing.
From an infrastructure point of view, the regulation says organisations must treat their network and cloud providers as essential parts of service delivery. IT teams should make sure providers go beyond just offering a service-level agreement and also give clear information about how their systems are built, managed, and secured.
Security by design in network infrastructure
To build security by design, start by choosing infrastructure platforms that follow well-known industry standards. When reviewing a network provider, IT teams should look for signs of a "born-in-the-cloud" or "security-first" approach. This shows the platform was built to work in high-risk, tightly regulated settings.
Key indicators of a security-by-design approach include:
• Identity and access governance — Providers should have strong identity and access management (IAM) features, such as multi-factor authentication (MFA); detailed, role-based access control (RBAC); and Policy Based Access Control (PBAC). This helps make sure only authorised people can change important network settings.
• Encrypted connectivity — Security by design means data must be protected both while moving and when stored. Network providers should make it easy to use encryption across multi-cloud and hybrid setups without making operations more complicated.
• Independent validation — Security claims need to be supported by third-party audits. Certifications like SOC 2 Type II, which cover security, availability, and confidentiality, are important standards. These reports give the proof needed for the due diligence required by DORA.
Building for operational resilience
Operational resilience means a company can handle, respond to, and recover from technology problems. For DORA, this means the network should not have a single point of failure. A resilient setup is usually spread out so if one part fails, traffic is rerouted to keep services running.
IT teams should choose providers that focus on high availability as a key part of their services. This means having constant monitoring and alerts to catch problems early. The provider should also have a clear and tested incident response plan. DORA requires financial institutions to report major ICT incidents to regulators quickly, so the network provider must be able to supply the needed data and logs for fast investigation and reporting.
Managing third-party risk and oversight
A major challenge with DORA is the extra oversight of third-party providers. Financial organisations now have to include clear contract terms about oversight and audit rights. This need for transparency can be hard for some traditional technology providers to handle.
When choosing an infrastructure partner, organisations should pick providers with clear processes for handling compliance questions. This means they can share security policies, operational procedures, and proof of regular penetration testing under non-disclosure agreements. The provider should act as a partner, helping the customer meet regulatory requirements, not just supplying a technical service.
The role of Infrastructure-as-a-Service (IaaS)
As financial institutions update their networks, many are choosing Infrastructure-as-a-Service (IaaS) models to handle the complexity of multi-cloud environments. These platforms connect on-premises data centres with different cloud service providers, acting as the system’s central hub.
To meet DORA requirements, an IaaS platform must show it does not create new risks. It should be built on a well-known cloud infrastructure that already meets strong security standards. Using a resilient IaaS model helps IT teams see their whole network clearly, making risk management and compliance easier.
Practical steps for IT teams
To get ready for DORA, IT and risk management teams should take these practical steps with their network providers:
1. Conduct comprehensive due diligence — Check current and potential providers to make sure they meet DORA’s rules for security controls, incident response, and resilience testing.
2. Audit contractual arrangements — Make sure contracts clearly state audit rights, service levels, and the provider’s duty to help during a regulatory inquiry.
3. Evaluate multi-cloud strategy — Check if your current network setup allows you to quickly move workloads between cloud providers if one goes down.
4. Establish clear reporting lines — Decide how the network provider will communicate during an incident and what information they will give to support your reporting needs.
Looking forward
DORA is an ongoing operational process, not a one-off project. As regulations change, the need for operational resilience will only grow. Financial institutions that focus on security by design and pick infrastructure partners who value transparency and reliability will be better prepared for these changes.
In the end, resilience is something everyone shares. The financial organisation is still responsible to the regulator, but its compliance success depends on its technology providers. By choosing providers who see compliance as a key part of their design, organisations can build a digital foundation that meets DORA and supports the future of digital finance.
Joe Peck - 23 April 2026
Exclusive
Features
News in Cloud Computing & Data Storage
How to define the right sovereign cloud strategy
In this exclusive article for DCNN, Joe Baguley, CTO EMEA at Broadcom, gives his insight into how a workload-first approach to sovereign cloud, underpinned by data classification, flexible architecture, and strong partnerships, is reshaping European digital competitiveness:
Reclaiming control and competitiveness
Across Europe, governments and enterprises alike are increasingly recognising that data control holds the keys to innovation. This means a change in attitudes towards cloud sovereignty; it’s no longer seen as a simple compliance factor, but as a top priority for competitiveness and trust.
The European Union is taking steps to support this shift, placing greater emphasis on sovereign infrastructure as part of its broader digital strategy. A clear example is the €180 million (£156 million) tender launched by the European Commission through its Cloud III Dynamic Purchasing System, aimed at procuring sovereign cloud services for EU institutions.
To ensure cloud sovereignty, the first step is preparation: organisations need a clear understanding of where their data resides, how it moves, and who controls it. Answering these questions requires a clearly defined strategy, one that aligns workloads with the most appropriate cloud environments and establishes effective data governance. Importantly, it has to support the development of flexible cloud architectures capable of meeting regulatory demands while still enabling innovation.
Designing cloud strategies around workload needs
At the heart of a successful sovereign cloud strategy lies a simple principle: placing the right workload in the right environment. There is no single solution that fits all applications. Enterprises must align each workload with the cloud environment that best meets its compliance, operational, and performance requirements to determine whether it belongs in a public, private, or sovereign cloud. Some applications may thrive in a hyperscaler environment, while others require the control and security of a sovereign setup.
This reality has made hybrid cloud strategies the norm. Over the past decade, many organisations initially committed to a single hyperscaler for all workloads only to realise that different applications have different requirements. Today, IT leaders increasingly need to adopt a ‘right workload, right place’ mindset, recognising that some applications may remain on premises, others run optimally in public clouds, and some require sovereign environments for regulatory or operational reasons. This hybrid approach enables organisations to balance innovation with control while avoiding vendor lock-in and making more effective use of the strengths of different cloud ecosystems.
Data classification comes first
Of course, organisations cannot secure or govern what they do not fully understand. Comprehensive data classification is a critical first step. Misclassified data is a frequent source of compliance risk and over-classification, often a product of risk aversion, which can create extra operational complexity and cost. Many organisations treat all data as highly classified simply to be safe, but this can lead to over-investment in secure infrastructure where it is not needed.
Mapping data flows across borders and providers is equally important. Compliance blind spots often appear when data is inadvertently stored or processed in jurisdictions with restrictive data laws. Understanding where sensitive data resides, how it moves, and which regulations apply is essential to reducing risk, demonstrating accountability, and maintaining trust with partners and customers. Retrofitting compliance into existing infrastructure is costly and complex; embedding that understanding into cloud architecture from the outset is far more efficient.
Building flexibility into architecture
Flexibility is the cornerstone of effective sovereign cloud implementations. Architectures built for interoperability and portability allow workloads to move seamlessly across private, public, and sovereign clouds.
This adaptability is vital for risks posed by geopolitical or regulatory change. Hyperscalers cannot always guarantee sovereignty due to extraterritorial legislation such as the US CLOUD Act, which permits government access to data held by American companies abroad. By contrast, working with local cloud operators enables enterprises to maintain jurisdictional control over their data while still leveraging the latest technology.
Moreover, working with local cloud operators can provide additional technological sovereignty benefits ranging from the investment to the local ecosystem and industrial base, all the way to addressing supply chain concerns, promoting interoperability, avoiding vendor lock-in, having stronger operational control, and managing dependency concerns.
Sovereignty should be viewed not as a constraint, but as a design principle guiding infrastructure, data placement, and application deployment. Organisations that prioritise adaptability can balance regulatory compliance with innovation and long-term strategic growth.
Partnerships powering sovereign cloud
Partnerships also play a pivotal role. No single vendor or platform can solve sovereignty challenges by themselves and, in the current interconnected supply chain, there does not exist a perfect vertical integration of suppliers within one region.
Open source is often presented as a solution to more autonomy. The reality, however, is that open source solutions create questions on code providence, reliability of a solution when deployed at scale, and different dependencies on support.
The most successful sovereign cloud environments combine global technology providers, local operators, and trusted EMEA partners (such as evoila and Arvato). This collaborative approach not only strengthens compliance and transparency, but also accelerates innovation by ensuring that governance does not become a barrier to progress. Meanwhile, the presence of a local ecosystem guarantees the ability to operate and support solutions with a high degree of autonomy.
As regulatory and geopolitical landscapes evolve, organisations that foster open dialogue across their supply chain and internal teams will be best placed to adapt. Sovereignty is as much about alignment, strategic choices, and accountability as it is about infrastructure.
From compliance requirement to strategic asset
Sovereign cloud has moved beyond a purely compliance-driven requirement and is increasingly becoming a source of strategic advantage. Organisations that commit to the ‘right workload, right place’ mindset and have clear data classification, flexible architecture, and prioritise interoperability are the ones that will have a competitive advantage. This approach allows organisations to scale globally whilst remaining aligned to regulatory and geopolitical shifts.
Sovereignty is an enabler of AI and should be treated as such.
Joe Peck - 20 April 2026

Head office & Accounts:
Suite 14, 6-8 Revenge Road, Lordswood
Kent ME5 8UD
T: +44 (0)1634 673163
F: +44 (0)1634 673173